Alibaba’s Qwen AI caught trying to contact server in China
But there’s not much evidence this is anything more than echoes of unsanitized training data Continue reading Alibaba’s Qwen AI caught trying to contact server in China
Collaborate Disseminate
But there’s not much evidence this is anything more than echoes of unsanitized training data Continue reading Alibaba’s Qwen AI caught trying to contact server in China
Mozilla launched a new ad campaign for Firefox that leverages early internet nostalgia in a bid to win back users who switched browsers. “Today’s internet tracks you, interrupts you, and asks for permissions it already took. But it wasn’t always that w… Continue reading Firefox Tries to Bring Back the Internet’s ‘Good Old Days’
iOS 27.2 is the first major update for the current OS. Here’s what’s inside and what happened to iOS 27.1. Continue reading Apple’s iOS 27.2 update offers major Siri AI upgrades, dual camera support for FaceTime
Which iPhones support iOS 27? See the full compatibility list, Apple Intelligence requirements, missing features, and whether you should upgrade.
The post Which iPhones Support iOS 27? Full Compatibility List and Missing Features appeared first on Tech… Continue reading Which iPhones Support iOS 27? Full Compatibility List and Missing Features
A ‘strong illustration of the risks associated with failing to rotate a potentially exposed key’ Continue reading LiteLLM supply chain attack started with an exposed master key
A string of hacking incidents by rogue AI agents also has raised fears the technology will slip free of human control to carry out harmful, life-threatening tasks.
The post Anthropic Files for Potentially the Biggest IPO Ever as CEO Warns of Risk to Hu… Continue reading Anthropic Files for Potentially the Biggest IPO Ever as CEO Warns of Risk to Humanity From AI
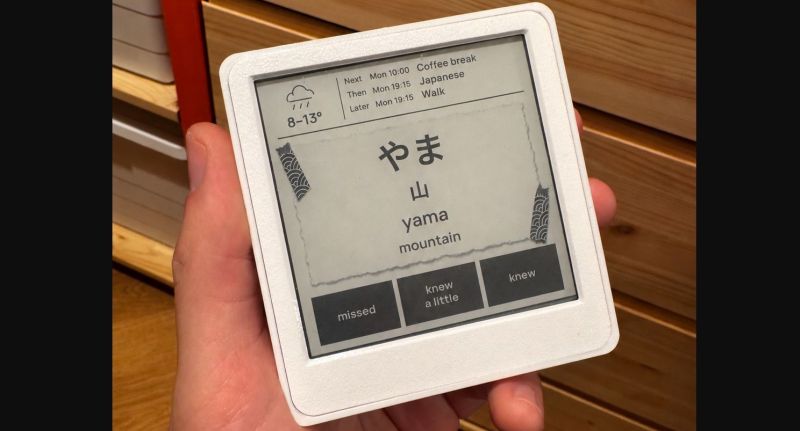
Learning a new natural language can be a daunting proposition at the best of times, with repetition and immersion generally considered to be the best ways to build up not …read more Continue reading Practice Japanese on an Inkplate 4Tempera eInk Device
Instagram is testing a new longform, horizontal video format called “Features” as it pushes further into YouTube territory and expands its presence on TVs. The Verge reports: Instagram boss Adam Mosseri has been against doing longform video on the plat… Continue reading Instagram Chases YouTube With a Push For Longer, Widescreen Videos
Apple is rolling out version 27.2 of its software lineup today, bringing new languages and other improvements to Siri AI, Apple Pencil support for the new iPhone Duo, and more.
The post Apple Releases Version 27.2 of iOS, iPadOS, macOS, watchOS, and tv… Continue reading Apple Releases Version 27.2 of iOS, iPadOS, macOS, watchOS, and tvOS
vsomeip, COVESA’s open source implementation of the SOME/IP automotive communication middleware, contained a memory allocation vulnerability present in versions 3.7.3 and below. A vsomeip reliable (TCP) SOME/IP endpoint grows its receive buffer to an attacker-declared message size before validating that the declared bytes have actually been received, allowing a remote, unauthenticated peer to exhaust host memory and deny service. The issue was reported publicly as COVESA/vsomeip issue #1009 and fixed in release 3.7.4 (2026-07-06).
CVE-2026-91141
vsomeip is a middleware implementation of the Scalable service-Oriented MiddlewarE over IP (SOME/IP) protocol, widely used for service-oriented communication between electronic control units (ECUs) in automotive and other embedded environments. A SOME/IP message begins with a 16-byte header that includes a 32-bit length field declaring the size of the message that follows.
A vulnerability was discovered in the handling of this length field on reliable (TCP) endpoints. When a message arrives, vsomeip grows its receive buffer to the size declared in the length field in order to read the incoming message, before confirming that those bytes have actually been received. In the default configuration, no size limit is applied to reliable endpoints, so a peer can declare a message size of up to roughly 4 GB and cause the receiver to allocate that memory. Because a freshly accepted connection reaches this path on its first message, no valid service, credentials, or SOME/IP authentication are required to trigger the allocation. The client endpoint contains the same behavior, where a malicious or compromised server can attack a connecting client.
Deployments that explicitly configure a reliable message-size limit are not affected.
This issue is publicly known. It was reported as COVESA/vsomeip issue #1009 (opened 2026-02-26) and fixed in release 3.7.4 (released 2026-07-06).
A remote, unauthenticated peer can force the host to allocate an attacker-chosen amount of memory, up to approximately 4 GB per connection, by sending a single short message on a normal TCP connection to any reachable reliable SOME/IP endpoint in the default configuration. On a memory-constrained node this can terminate the service outright: a service limited to 1.5 GB was OOM-killed by a single 16-byte message claiming a 3 GB payload. On a memory-rich host, the allocation for a single connection is released when the connection closes, so sustained memory exhaustion and denial of service follow from holding or repeating connections, each forcing its own allocation.
Upgrade to vsomeip 3.7.4 or later. This issue is fixed in release 3.7.4 (released 2026-07-06). The fix replaces the unlimited compile-time default (MESSAGE_SIZE_UNLIMITED) with a bounded DEFAULT_MAX_MESSAGE_SIZE of 10 MiB, so reliable endpoints reject an oversized declared length before growing the receive buffer even when no limit is explicitly configured. The release also adds a regression test for an oversized length field. The issue and fix are tracked publicly in COVESA/vsomeip issue #1009.
Deployments that cannot upgrade immediately should apply the following mitigations.
Deployments can explicitly set max-payload-size-reliable (or the equivalent per-service reliable message-size limit) to a value appropriate for the service. Endpoints with such a limit configured reject oversized declared lengths and are not affected by this issue. This is the most effective mitigation available without upgrading.
Because the vulnerability is reachable by any host that can open a TCP connection to a reliable SOME/IP endpoint, exposure should be minimized through network segmentation. Reliable endpoints should be confined to trusted, isolated in-vehicle or lab networks, and firewall or access-control rules should limit connectivity to known, authorized peers. SOME/IP endpoints should never be exposed to untrusted or external networks.
Operators should monitor for anomalous memory growth on services offering reliable endpoints and for unexpected or repeated inbound TCP connections to SOME/IP ports, which may indicate attempts to exploit this vulnerability.
Thank you to the Jaafer Rahmani for reporting this vulnerability. This document was written by Alexander Curtis.