Anthropic merges Claude chat and Cowork into one
From Claude to Cowork and back again – plus, Anthropic’s all-new Claude Docs. Continue reading Anthropic merges Claude chat and Cowork into one
Collaborate Disseminate
From Claude to Cowork and back again – plus, Anthropic’s all-new Claude Docs. Continue reading Anthropic merges Claude chat and Cowork into one
The update lets you contact VIPs with a tap and adds scam protection. Continue reading How September’s Pixel Drop changes the way you call and message important contacts
Microsoft will hold a Windows and Surface event in San Francisco on October 7, featuring CEO Satya Nadella and NVIDIA CEO Jensen Huang.
The post Microsoft to Hold Surface and Windows Event on October 7 appeared first on Thurrott.com.
Continue reading Microsoft to Hold Surface and Windows Event on October 7
The $149 AirPods 5 add stem volume control, broader charging support, a Find My case speaker, and longer battery life over the $129 version.
The post AirPods 5: Should You Pay $20 More for the Wireless Charging Case? appeared first on TechRepublic.
Continue reading AirPods 5: Should You Pay $20 More for the Wireless Charging Case?
Mozilla and Mistral announced today that they have partnered to bring AI capabilities to Firefox Smart Window.
The post Mozilla Partners with Mistral on Firefox Smart Window appeared first on Thurrott.com.
Continue reading Mozilla Partners with Mistral on Firefox Smart Window
A critical security flaw in Issabel Framework, a web-based framework for the open-source unified communications PBX software, has come under active exploitation.
The vulnerability in question is CVE-2026-89026 (CVSS v3.1 score: 9.8/CVSS v4.0 score: 9…. Continue reading Attackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command Execution
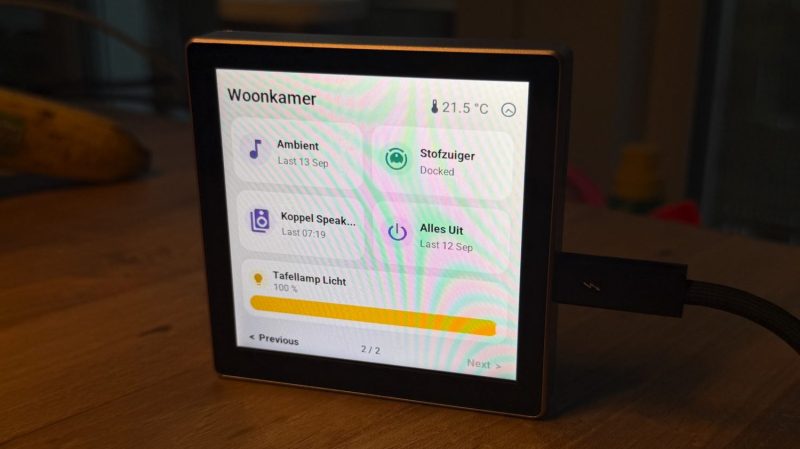
Home Assistant is a great way to rig up and manage your smart home and its many and varied devices. You can of course control the system from your smartphone …read more Continue reading A Cheap and Easy Control Screen For Home Assistant
Enterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy Ghouls, according to multiple reports from Kaspersky.
The cybersecurity vendor said it has identified attacks mounted by Nig… Continue reading Three Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and Wipers
A vulnerability exists in Sentry Seer when the system is configured to automatically hand issues to a coding agent for remediation. Successful exploitation results in arbitrary code execution within the coding‑agent environment and access to connected source repositories. This vulnerability is tracked as CVE-2026-90999.
Sentry is a software error‑monitoring and performance‑tracking platform used by developers to detect, diagnose, and understand issues in their applications. It collects telemetry such as exceptions, stack traces, logs, and performance data from applications. Built into Sentry, Seer acts as an automated debugging assistant that converts telemetry into actionable remediation steps and can hand off issues to an integrated coding agent to propose code fixes.
Because Sentry front-end projects commonly expose a public DSN (Data Source Name) to allow browsers to submit this telemetry, an attacker can craft and submit malicious events through this public endpoint. When Seer is enabled to automatically pass issues to a coding agent, these attacker-supplied events can traverse multiple trust boundaries. Ultimately, malicious event fields propagate through Seer’s analysis pipeline, transforming into untrusted instructions that the privileged coding agent may execute.
The vulnerable workflow is as follows:
* Sentry ingests attacker‑generated exception events submitted through the public DSN.
* Seer evaluates whether the event represents an issue eligible for automated remediation.
* Seer generates a root‑cause analysis that uses attacker-controlled event fields, including exception messages, stack traces, source context, and breadcrumbs.
* The generated analysis is embedded directly into the initial prompt provided to the coding agent.
* The coding agent interprets the fabricated analysis as a legitimate description of the victim’s codebase.
* During its investigation, the coding agent downloads and executes a package controlled by the attacker.
* The package executes within the coding‑agent environment prior to any human review of a pull request.
Successful exploitation may allow arbitrary code execution in the coding‑agent environment that processes the affected repository.
At the time of this writing, no vendor‑supplied patch information has been provided. Mitigations may include disabling automated remediation flows, restricting coding‑agent package installation, or disabling Seer handoff until a fix is available. Additional defensive filtering of telemetry content before Seer analysis may also reduce risk.
Thank you to Nikita Benkovich and Vitalii Valkov, agyn for reporting this vulnerability. This document was written by Bob Kemerer.
iPhone 18 Pro adds a new camera, faster chip, better battery life, and more storage. Here’s whether those upgrades are enough to leave the 17 Pro behind.
The post iPhone 18 Pro vs iPhone 17 Pro: Should You Upgrade? appeared first on TechRepublic.
Continue reading iPhone 18 Pro vs iPhone 17 Pro: Should You Upgrade?