Here’s how broken today’s web will feel in Chrome’s secure-by-default future

Last week Google announced some changes to Chrome, specifically that come January 2017, practices like this are going to start resulting is browser warnings:
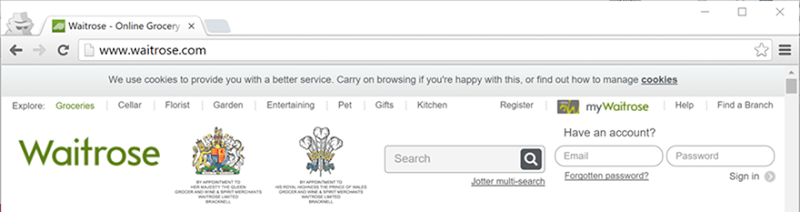
That’s just one of many such examples I’ve called out in the past and frankly, I have about zero sympathy for those who are doing this

Continue reading Here’s how broken today’s web will feel in Chrome’s secure-by-default future→

The “Have I been pwned” API rate limit has been brought forward – here’s why

Three weeks ago today, I wrote about implementing a rate limit on the Have I been pwned (HIBP) API and the original plan was to have it begin a week from today. I want to talk more about why the rate limit was required and why I’ve had to bring

Continue reading The “Have I been pwned” API rate limit has been brought forward – here’s why→

Self-hosted vBulletin – you’re doing it wrong! (and why you should be using managed hosting services)

Another day, another data breach:

Full news on the GTAGaming breach is here: https://t.co/KuNSuol442 (vBulletin again)

— Troy Hunt (@troyhunt) August 23, 2016

Yesterday it was a different one:

vBulletin… “Epic Games: Information Regarding Recent Forum Compromise” https://t.co/YqQlSRbtLU

— Troy Hunt (@troyhunt)

Continue reading Self-hosted vBulletin – you’re doing it wrong! (and why you should be using managed hosting services)→

Understanding account enumeration, the video tutorial edition

I’ve been running my Hack Yourself First workshop all over the world where I talk to software developers about various security risks which they then get to exploit firsthand. It’s a lot of fun and very hands on and practical which inevitably means spending time looking at real world implementations

Continue reading Understanding account enumeration, the video tutorial edition→

Website enumeration insanity: how our personal data is leaked

I’ve just wrapped up a couple of Hack Yourself First workshops down closer to home in Australia and true to usual form, attendees found some absolute zinger security implementations. Previous workshops have found various vulnerabilities ranging from realestate.com.au’s lack of HTTPS in their Android app (pro tip: don’t

Continue reading Website enumeration insanity: how our personal data is leaked→