MVP, round 6!

Each year since 2011, on April first (yeah, I know…), I’ve looked for one of these to land in my inbox and fortunately, this year didn’t disappoint:

Congratulations! We are pleased to present you with the 2016 Microsoft® MVP Award! This award is given to exceptional technical community leaders who actively share their high quality, real world expertise with others. We appreciate your outstanding contributions in Visual Studio and Development Technologies technical communities during the past year.

The MVP program has been an enormously fulfilling thing to be a part of these last five years. It’s been great for the connections I’ve made, the access to folks in Microsoft and the community engagements it’s lead to, particularly in my post-corporate life as an independent. Now yes, I’ve been misquoted as “Troy Hunt from Microsoft” many, many times as a result but frankly, that’s been the only downside.

For those wondering, this is independent of my role as a Microsoft Regional Director. I’ll still go through the annual MVP renewal process which looks at what community contributions I’ve made and then (hopefully) the RD thing will continue to tick over on a bi-annual basis.

Thanks everyone who continues to read this blog, watch my Pluralsight courses, come to my conference talks and do the things that you do to help me have such a fulfilling career 🙂

Continue reading MVP, round 6!→

Posted in MVP

The world needs more stupid security researchers – join me!

I love this Google Play store review of the NissanConnect app which had such terrible security issues recently:

I may print and frame this: pic.twitter.com/P0hu7E08GQ

— Troy Hunt (@troyhunt) March 17, 2016

I join a long line of stupid security folks who’ve messed things up for other people. Sometimes people have been unable to purchase things just because a stupid researcher found that credit cards may be stolen. Or unable to use government services because another stupid researcher found personal info may be exposed. How inconvenient!

It’s like that stupid doctor I saw that time who told me I had pneumonia and made me rest up. What a dick.

Or the stupid local government that makes us put a fence around the pool. They’re my kids running around the place, dammit!

Whilst there is stupid security, we need more stupid security researchers. Not everyone will always agree with you, but we need you to help make the web a safer place. As a permanent reminder that sometimes you need to upset the minority in order to better protect the majority, I did indeed print and frame that app store review:

Photo 30-03-2016, 16 07 41

People will get angry. They’ll blame you for the ills created by others. They’ll accuse you of all sorts of things with reckless, irrational abandon. If you’re cranky about negligence such as this being called out then just be patient, there’s much more for you to be mad about yet.

Don’t be Melvyn. Be bold and stupid and whatever else it takes to approach security like this ethically, yet effectively. The world needs more stupid security researchers!

Continue reading The world needs more stupid security researchers – join me!→

New Pluralsight course: Ethical Hacking, Denial of Service

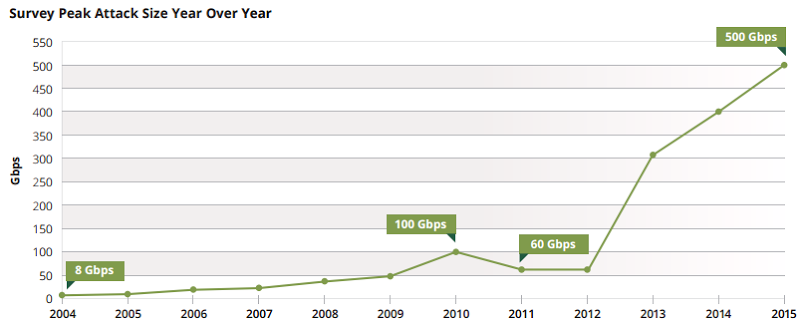
I’ve just launched my latest Pluralsight course titled Ethical Hacking, Denial of Service but before I explain what’s in it, let’s kick off with some trivia: DDoS attacks have increased massively in size in recent years:

DDoS attacks going from 60Gbps in 2011 to 500Gbps in 2015

This is from Arbor Networks’ latest Worldwide Infrastructure Security Report and that was current in October when the study was done. Now, it’s not so current:

A 602Gbps attack

By the time you read this, we may well be at 700 or 800 or who knows where because the trend is very consistently “up and to the right”, as they say. But it’s not just the scale of the attacks which is alarming, it’s the cost. We may think of a DDoS attack as being a simple temporary outage (or a peaceful protest, as some would like to see it), but have a look at how much Arbor found it actually costs organisations in their report:

DDoS costing up to $20k per minute of outage

So about two thirds of company take a hit of $30k an hour or more. 14% of them were seeing costs upwards of ten times that – $300k per hour because of DDoS!

But here’s the other crazy thing about this class of attack – it’s easy, it’s cheap and you don’t need any specific app flaws in order to seriously mess with a site. Here’s a perfect example of how easily DDoS is, go and check out this site (turn your speakers way up first!):

The booter.xyz service

I’m not normally in the habit of linking through to malicious sites, but “booters” are so prevalent and easily accessible on the clear web that you’ll find them within minutes anyway if you want to. The crazy thing with the booters is the sheer prevalence of them and the ease with which they seem to be spun up. For example, the Lizard Squad service of late 2014 which proved to be rather effective at taking down the likes of Sony’s PSN and Microsoft’s Xbox Live. Even kids in their bedrooms are spinning up DDoS services these days:

Now to be clear, I’m not exactly sure how effective Christa’s service really is, but there’s something about DDoS that really appeals to kids. Part of it is likely that they’re just so easy to execute in an impactful way; not only are there many DDoS as a service offerings out there (DDoSaas?), they also don’t need any specific vulnerabilities in the target site in order to cause damage. No SQL injection or XSS or enumeration risks or anything like that, they merely need a site which can handle less traffic than they can send it.

DDoS has also become a favourite with this genre that we know as the hacktivist. For example, we’ve seen successful attacks based on philosophical differences such as #oppayback in the wake of PayPal and co refusing to accept donations to Wikileaks. The legalities of this action aside (and I’ll come back to that), you can understand the ire the hacktivists felt in the wake of PayPal’s decision. Likewise, there probably wasn’t a whole lot of sympathy when hactivists DDoS’d Scientology and I suspect next to zero sympathy when it was Westborough Baptist church being hit.

But the ease of this class of attack also makes for some pretty unreasonable action on behalf of adversaries. For example, just a couple of months ago Nissan was DDoS’d. Why? No, not because they build cars with security flaws, rather it was because of the whales. Hang on – what? This is not because Nissan is upholstering cars in whale skin or testing airbags on them or anything whacky like that, it’s because Nissan is Japanese and there remains “scientific research” there which involves harpooning them. (It’s unclear how scientific turning them into sushi is, but I digress.) The point is that Nissan themselves almost certainly have nothing to do with whaling yet they copped a rather effective DDoS there for a while.

Another reason DDoS attacks remain rampant particularly via hacktivists is that they frequently don’t believe there’ll be any recourse. I recently watched the We Are Legion documentary (not sensational, but worthwhile viewing IMHO), and it was interesting to see just how unaware so many of those involved in the aforementioned #oppayback attacks were. They gave no thought to the fact that what they were doing might be illegal and could have serious consequences. Being entirely objective about it, you can see how they might draw that conclusion; they’re sitting there in their bedrooms firing up a tool like LOIC (a favourite with hacktivists) and then just… going outside and playing. No seriously, here’s a tutorial by Anonymous that tells you to do just that:

Ok, this is funny for many reasons yet it does demonstrate how eager especially kids or young adults are to jump on the DDoS bandwagon. In the aforementioned documentary, many of those interviewed talked about how DDoS was just a form of protest, in fact even their lawyer was quite adamant they were just exercising their freedom of speech rights. The problem is though, when you’re costing an organisation thousands of dollars by the minute, you’re actually doing serious damage and with that comes serious consequences. A few years back I wrote What is LOIC and can I be arrested for DDoS’ing someone? because I was amazed at just how many people thought they couldn’t be arrested for it!

I could go on about DDoS because it’s a genuinely fascinating topic, but I do want to touch on the point of writing the post in the first place which is to launch my latest (and 21st) Pluralsight course titled Ethical Hacking, Denial of Service. This is now the 6th course in the Ethical Hacking series and I decided to break it down into four modules like so:

  1. Understanding Denial of Service Attacks: How this class of attack has grown so rapidly in recent years and the impact it’s having on organisations, as well as some really neat visualisation of attacks such as the Norse map.
  2. Attack Techniques: There’s a lot more to denial of service attacks than a bunch of people pointing LOIC at a site. SYN floods, ICMP and UDP attacks, DNS amplification and even the man on the side style of attack we saw against GitHub last year to name just a few.
  3. Tools and Services: Obviously I touch on LOIC (and it’s web-based counterpart JS LOIC) and I then delve into the operations of booters as mentioned above and the whole DDoSaaS class of offering. In fact I even do a walkthrough of one of these which gives some insight into just how polished these services have become.
  4. Defending Against Attacks: Given the course is aimed at your ethical class of professional, I naturally spend a bunch of time talking about how to limit the effectiveness of these attacks. It’s never foolproof, but there’s a lot that can be done to lessen the blow of an attack.

That’s it for DDoS, the course is now live and ready to be viewed – enjoy!

Continue reading New Pluralsight course: Ethical Hacking, Denial of Service→

Understanding CSRF, the video tutorial edition

Cross site request forgery is one of those attacks which remains enormously effective yet is frequently misunderstood. I’ve been running a bunch of security workshops for web developers around the globe recently and this is one of the topics we cover that often results in blank stares when I first ask about it. It usually unfolds that the developers have multiple resources at risk of a CSRF attack and if it’s not a classic web form style resource, then it’s frequently an API somewhere (you’re passing anti-forgery tokens to any APIs you wouldn’t want fraudulently called, right?!)

I thought I’d record a quick (ok, half an hour is still quick for me!) and unedited walkthrough of the mechanics of CSRF and how ASP.NET deals with it in both MVC and Web Forms. The .NET bits are just examples of how anti-forgery tokens in hidden form fields and cookies work though so don’t worry if you live in another web stack, it’s the same fundamental defence. Here’s the vid:

For a great example of nasty CSRF and an attack style we’ve seen many times before now, check out how an attack campaign compromised 300,000 home routers, alters DNS settings.

If you’d like to have a play with CSRF yourself, that form I used in the vid is here: http://evilcyberhacker.com/csrf.html

The site I use to demo it is here: http://hackyourselffirst.troyhunt.com

If you’d like to read about CSRF in more detail, check out my 2010 post (crikey, is it that long already?!) on OWASP Top 10 for .NET developers part 5: Cross-Site Request Forgery (CSRF). If you have Pluralsight access, it’s in my course of the same name for the .NET folks or my Hack Yourself First course if you’d like a technology agnostic view of it. If you don’t have Pluralsight, firstly, what’s wrong with you?! 🙂 And secondly, you can still get three months for free using this one neat trick… enjoy!

Continue reading Understanding CSRF, the video tutorial edition→

Request for feedback: Organisations using “Have I been pwned” data

Working on Have I been pwned (HIBP), I come across a lot of interesting things. Interesting people dealing in data breaches, interesting vulnerabilities in systems which have been compromised and interesting requests from people wanting the data. In fact, I was getting so many requests for data I ended up

Continue reading Request for feedback: Organisations using “Have I been pwned” data→

Request for feedback: Organisations using “Have I been pwned” data

Working on Have I been pwned (HIBP), I come across a lot of interesting things. Interesting people dealing in data breaches, interesting vulnerabilities in systems which have been compromised and interesting requests from people wanting the data. In fact, I was getting so many requests for data I ended up writing No, I cannot share data breaches with you where I very explicitly laid out how I wouldn’t give people their own record from a breach, I wouldn’t give the data to researchers and I wouldn’t trade data breaches. I still hold that view – nothing has changed there – but I’ve been receiving some requests recently for access to data which is causing me to stop, think and, well, write this blog post seek your feedback. Let me explain.

HIBP is used in a number of different ways by large organisations. Some of them rely on the public API to check the exposure of their users and notify them, many have domain subscriptions which send them a notification if one of their colleagues is in a breach and a small number are using the commercial callback implementation to notify them when an account they’re monitoring is impacted. However, there are a few things stopping other orgs from using the service in any of these ways, things I can’t overcome with the current model.

The barriers I’m hearing from organisations who would like access to the data to do good things (I cannot emphasise that point enough) are two-fold; service location and privacy. On the former, these orgs are typically European and are beholden to local legislation which doesn’t like their data being sent outside the EU and subscribing emails to or querying HIBP would do just that. I could stand up an EU instance of the service, but it doesn’t solve the next issue which is privacy. These companies are understandably worried about sending me any of their data. They don’t want a situation regardless of where the service runs where I know who their customers are and I totally get that – I’d have the same concern.

So it leaves me in somewhat of a quandary; these organisations want to do good things with the data but my existing constructs make that impossible. Let me talk about the sorts of things they want to do though as that will put things in more perspective and I’ll start with an example. Someone sent me this from Amazon just the other day, have a read:

From: security-update@amazon.com
Subject: Your Amazon password has been changed
Date: March 16, 2016 at 4:02:41 PM CDT
To: [redacted]

Hello,

At Amazon we take your security and privacy very seriously. As part of our routine monitoring, we discovered a list of email address and password sets posted online. While the list was not Amazon-related, we know that many customers reuse their passwords on several websites. We believe your email address and password set was on that list. For your security, we have assigned a temporary password to your account.

You will need to reset your password when you return to the Amazon.com site. To reset your password, click "Your Account" at the top of any page on Amazon.com. On the Sign In page, click the "Forgot your password?" link to reach the Amazon.com Password Assistance page. After you enter your email or mobile phone number, you will receive an email containing a personalized link. Click the link from the email and follow the directions provided. 

Your new password will be effective immediately. We recommend that you choose a password that you have never used with any website.

Sincerely,

Amazon.com
http://www.amazon.com

This is actually really cool – Amazon are sourcing data breaches then notifying their customers when they find a credential match. This isn’t entirely new, in fact I wrote about how both them and LinkedIn were doing it back in November. There are many fascinating things about this: Firstly, they’re actively acquiring data breaches, an activity that some have suggested is on the shady side of legal yet here we have some of the web’s largest properties doing it to do good things. Secondly, given that the vast majority of breaches have some form of cryptographic storage for passwords (even if it’s just plain old MD5), they’re either cracking hashes or hashing their customers’ passwords with the algorithm of the breached site when they log in (or register or change their password). It’s quite possibly the former as the individual who sent me the email above noted that it was an account he hadn’t used for years.

I can only see upsides to the likes of Amazon doing this. They’re decreasing the risk to the individual and they’re decreasing the likelihood of them having to deal with account takeovers by malicious parties. If they get onto this fast enough after a breach is found (and that’s always going to be the challenge), they have the ability to put a serious dent in the value of the data for those who wish to do harm.

All this brings me back to the requests I’ve been getting for access to HIBP data. These are coming from large names you’d recognise in various technology sectors and the common thread from these legitimate big players is that they genuinely want to improve the security of their existing customers. They want to do the same thing as Amazon and LinkedIn except they want the ability to consume that data “as a service”. But they don’t want the full data breach; they don’t want birth dates and genders and in a case like VTech, the names of people’s kids or for Ashley Madison, what your bedroom preferences are. They only want email addresses and passwords and in some cases, only just the email addresses.

I’ve thought of many different ways to do this without sending large volumes of data to the organisations keen on this approach. For example, I could have them send me a hash of the email they want to monitor and then hash each incoming email in a new breach and match based on those. In fact, this is already a suggestion in the HIBP User Voice but the problem is that I can still derive the original value of an address once I match it to one in a breach and they’re still “giving” me addresses which is against their rules. I’ve thought of just providing directions on where an org can obtain the breach from but not only is this not always possible (many are sent to me privately), there’d still be a bunch of processing work required on their behalf, work that I already do and they’d like to consume “as a service”.

The more I’ve thought about this, the more I keep coming back to one key principle: could this help data breach victims? Would it reduce the number of accounts they’ve reused credentials across getting compromised and increase their awareness of the risks they face? It’s an emphatic “yes” and the remaining questions about whether this should happen or not are related to the downsides. Would this violate their privacy? That’s largely dependent on how the organisation I send this to handles it. Could it be done securely? Certainly we have mechanisms to transfer data in a highly secure fashion, it potentially wouldn’t even need to touch the Azure-based HIBP service (i.e. could be distributed directly from the environment in which the processing is done).

Here’s what I’d like from you: On balance, is this a good thing for data breach victims? Which organisations should have access to this data? What controls would you put in place? Is this something that would be valuable to your organisation? Anything else?

If you’ve been following HIBP for any period of time, you’ll know that I’m super cautious around issues of privacy and using the data for good. The last thing I’d ever want is to have all sorts of issues arise that I’d never even thought of. It’s not a small thing either – I’d have to make it a commercial offering – and there’d be a significant time commitment from me not just to build the mechanism but also each and every time I process a data breach. An agreement in place with a consuming organisation would also need to strictly outline how the data may be used, for example only to provide services that improves the security of their existing customers and not to elicit business from new ones. But I think it has the potential to do good things in the right organisations, such as what you see above with Amazon.

Leave your comments below folks or if you want to share anything privately, see the contact page. I’d love to hear your feedback.

Update: Have a read of Nzall’s comment about hashing. This sounds like a good model for reducing the risk of abuse as the customer would need to hash and compare each and every email on their end, they could never simply pull the entire list of addresses from the breach.

Continue reading Request for feedback: Organisations using “Have I been pwned” data→