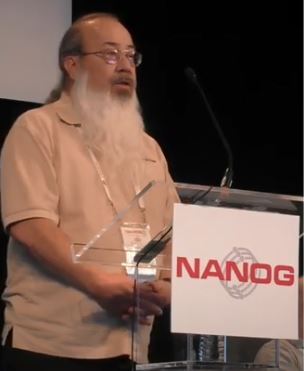
In Memory of Donald Smith, (Mon, Jul 27th)

Donald SmithLast week, we learned of the passing of our friend and fellow ISC Handler, Donald Smith. Don may not be a “household name” when it comes to Internet Security, but he was one of those people who steadfastly worked in the background and pushed us all to collaborate and do better. Don was not in it for the glory. Despite Don&#39&#x3b;s many impacts, his unwillingness to take credit never wavered. In some ways: If you never heard of Don, that was the reason why he was effective at what he did. And if you did hear of Don, or worked with him, you are probably saying that I am wrong: Everybody knew Don. If you were involved in a trusted sharing group, or if you were active in network security, you probably ran into Don at one point or another. If you remember Don: You did something right.

Continue reading In Memory of Donald Smith, (Mon, Jul 27th)→

Posted in Uncategorized

Cracking Maldoc VBA Project Passwords, (Sun, Jul 26th)

In diary entry “VBA Project Passwords” I explained that VBA project passwords in malicious documents don&#;x26;#;39;t hinder analysis: you can just extract the macros without knowing the password. It&#;x26;#;39;s only when you would perform a dynamic analysis with the step-by-step debugger of the VBA IDE, that the password would prevent you from doing this. But there are simple methods to remove the password, and then you can go ahead with your debugging.

Continue reading Cracking Maldoc VBA Project Passwords, (Sun, Jul 26th)→

Posted in Uncategorized

Compromized Desktop Applications by Web Technologies, (Fri, Jul 24th)

For a long time now, it has been said that “the new operating system is the browser”. Today, we do everything in our browsers, we connect to the office, we process emails, documents, we chat, we perform our system maintenances, … But many popular web applications provide also&#;x26;#;xc2;&#;x26;#;xa0;a desktop client: Twitter, Facebook, Slack are good examples. Such applications just replace the classic browser and use the API&#;x26;#;39;s to interact with the official website. Most applications are developed in a compiled language and are deployed as regular executable files.&#;x26;#;xc2;&#;x26;#;xa0;Others&#;x26;#;xc2;&#;x26;#;xa0;rely on web technologies or have a modular architecture that helps to add features via a system of plugins or modules.

Continue reading Compromized Desktop Applications by Web Technologies, (Fri, Jul 24th)→

Posted in Uncategorized